Compliance
Certification frameworks and evidence collection.
Nothing launched in this category yet.
Be the firstAbout Compliance
Compliance tooling has grown from a niche into a substantial category, driven by data protection regimes, security certification demands from enterprise buyers, and accessibility requirements becoming enforceable. The launches here cover evidence collection and audit readiness, privacy operations, policy management, vendor risk and accessibility auditing.
For a small software company, the compliance question usually arrives as a security questionnaire from a prospective customer, and the tools that automate certification readiness exist to answer it. What they genuinely do is collect evidence continuously — that access reviews happened, that machines are encrypted, that logs are retained, that changes were reviewed — so that an audit is a report rather than a scramble. That is real value. What they do not do is make you secure; they document controls you have implemented. A company that adopts the tool and not the controls has bought an expensive way to be audited.
Privacy operations is the other large piece: handling access and deletion requests, maintaining records of processing, managing consent, and tracking where personal data actually lives. That last one is the hardest and the most valuable, because most organisations cannot answer it, and every obligation depends on it. A tool that builds an honest inventory is worth more than one with better workflows over an incomplete map.
Vendor management matters more than it seems, because your obligations extend to processors you use. Knowing which vendors touch personal data, what agreements exist and what happens if one has an incident is basic and frequently absent.
Accessibility auditing deserves a specific note: automated scanners reliably catch perhaps a third of real issues. They find missing labels, contrast failures and structural problems, and they cannot tell whether a flow is operable by keyboard or whether the reading order makes sense. Automated tooling plus periodic manual testing is the honest approach; a green scanner score alone is not compliance.
As with everything in this area: software supports a compliance programme and does not constitute one, and obligations vary by jurisdiction, sector and the data you hold. Confirm your specific position with someone qualified.
From the blog
Reading on launching, ranking and compliance.
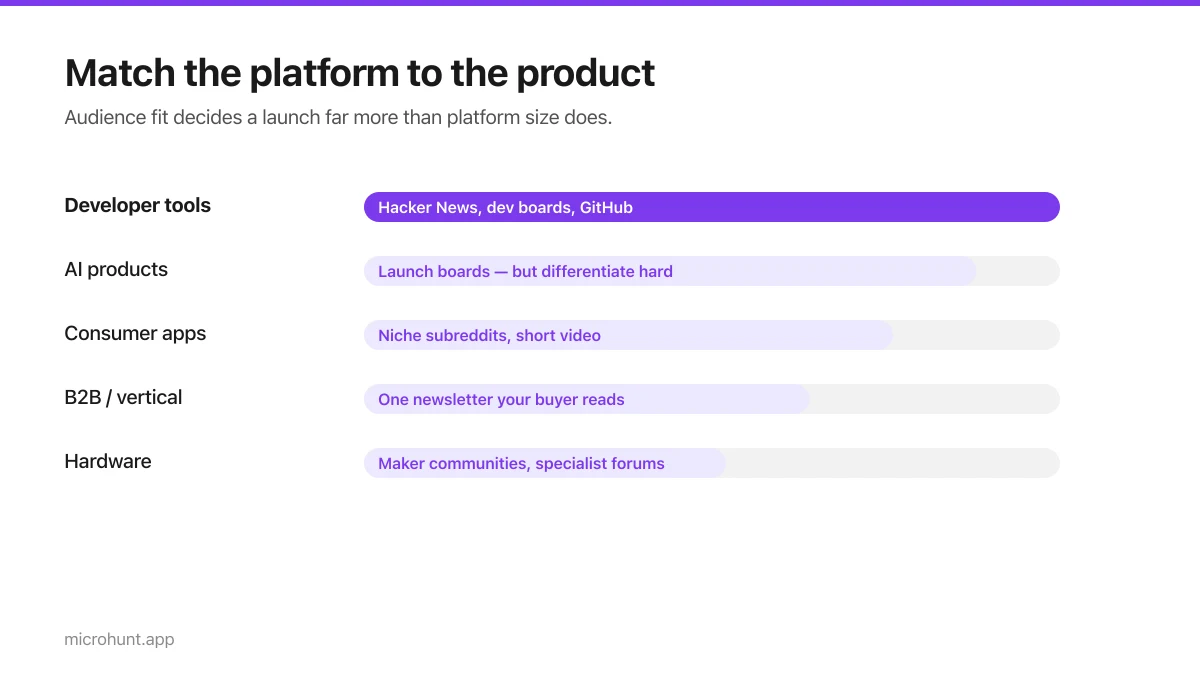
Best Product Hunt Alternatives for Launching in 2026
Where else to launch when Product Hunt is not the right fit — what each platform is actually good at, who shows up, and what it costs.
8 min read
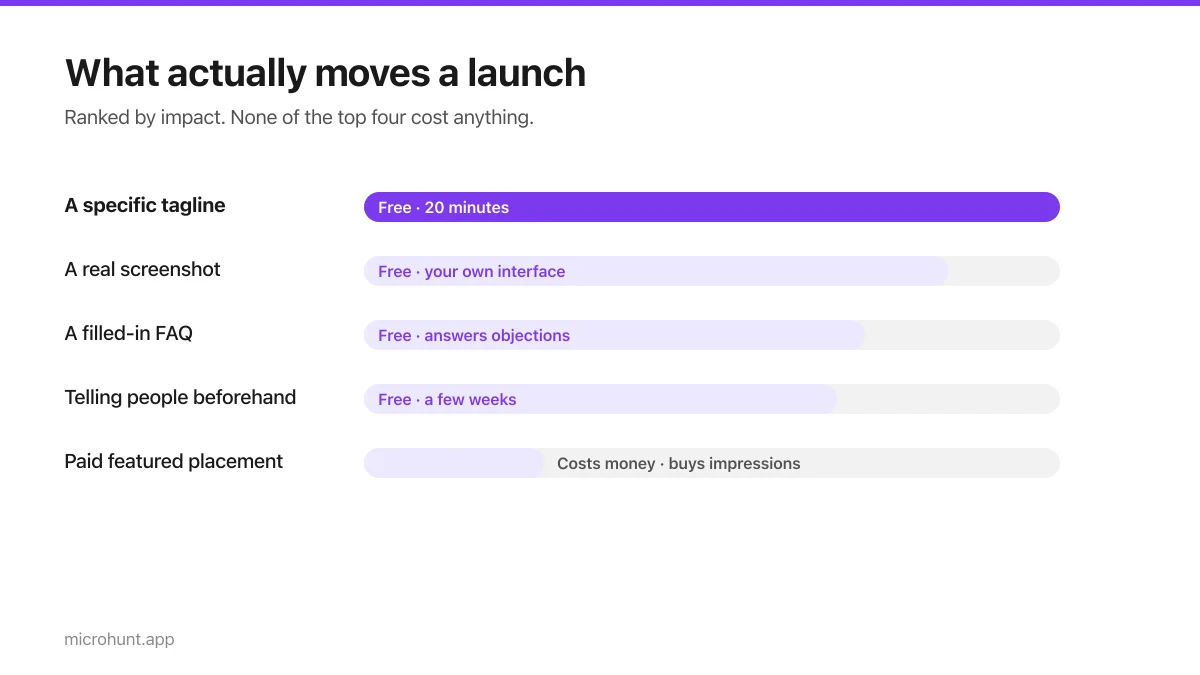
Free Launch Platforms for Indie Makers (No Budget Needed)
You do not need to pay to launch. Here are the places that are genuinely free, what each expects from you, and where paying is actually worth it.
7 min read
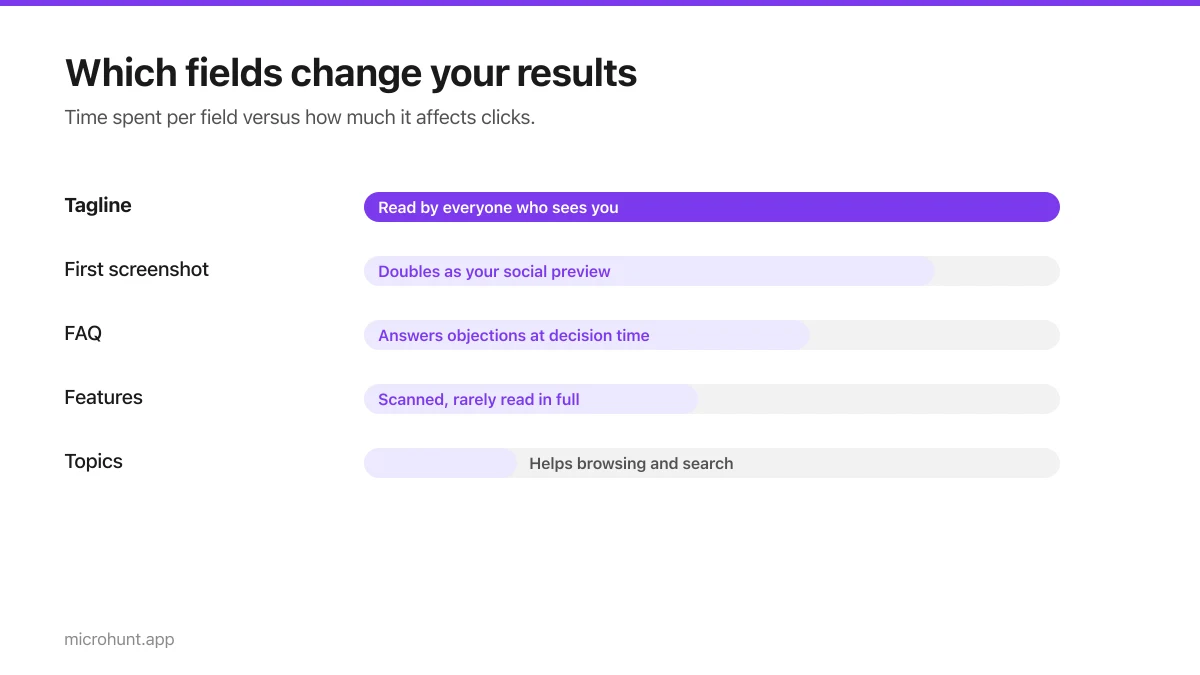
How to Submit a Product on Vuru (Step by Step)
A walk through the submission form, what each field does to your page, and the fields most people leave empty that they shouldn't.
7 min read
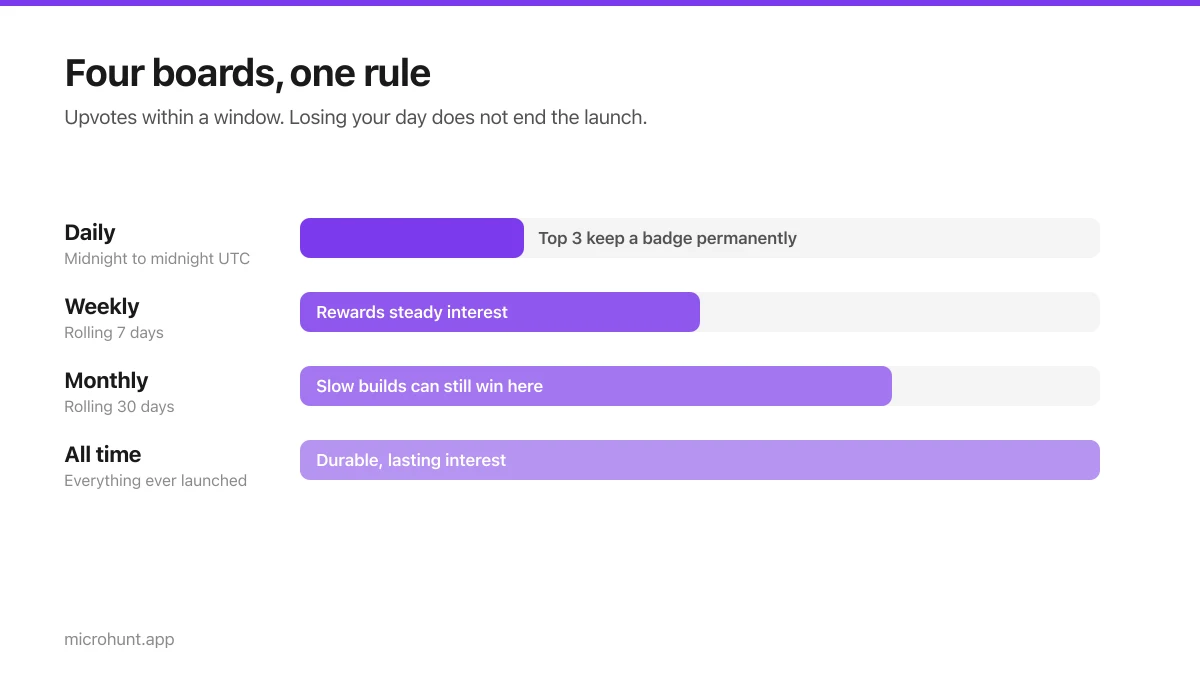
How Vuru Ranking Works (And How to Win a Badge)
Launch windows, upvotes, podium badges and what we do about vote manipulation — the whole ranking system explained plainly.
7 min read
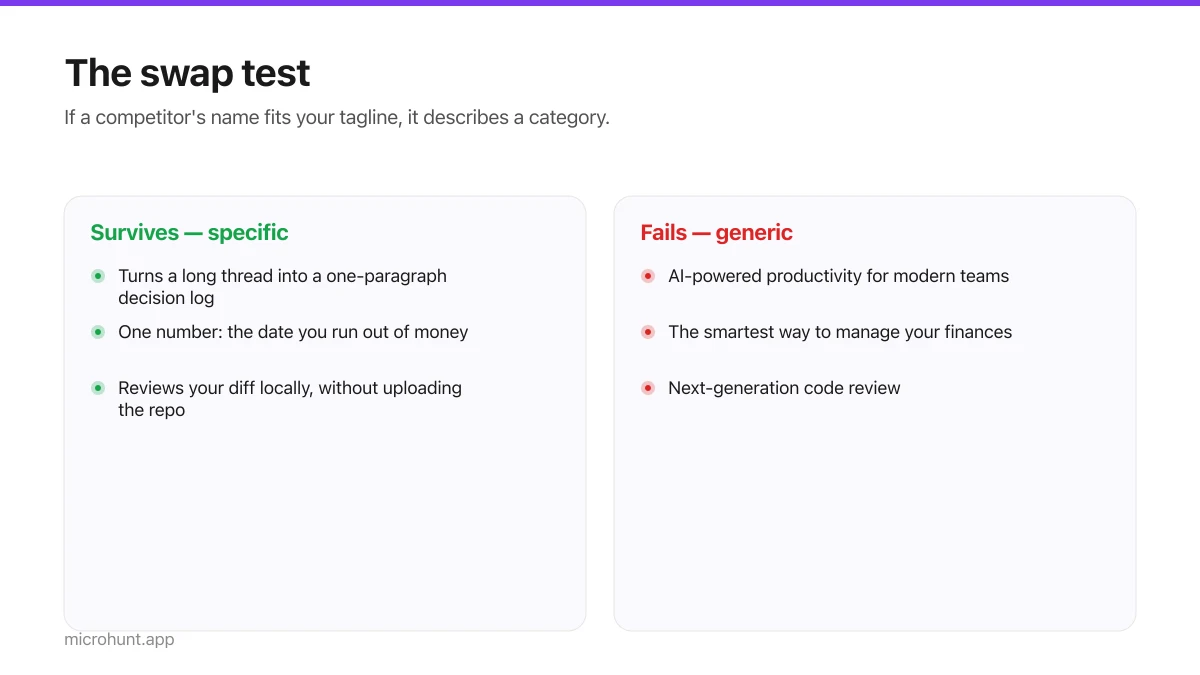
How to Write a Product Tagline That Actually Gets Clicked
The one line most people will ever read about your product, and a simple test for whether yours is doing any work.
7 min read
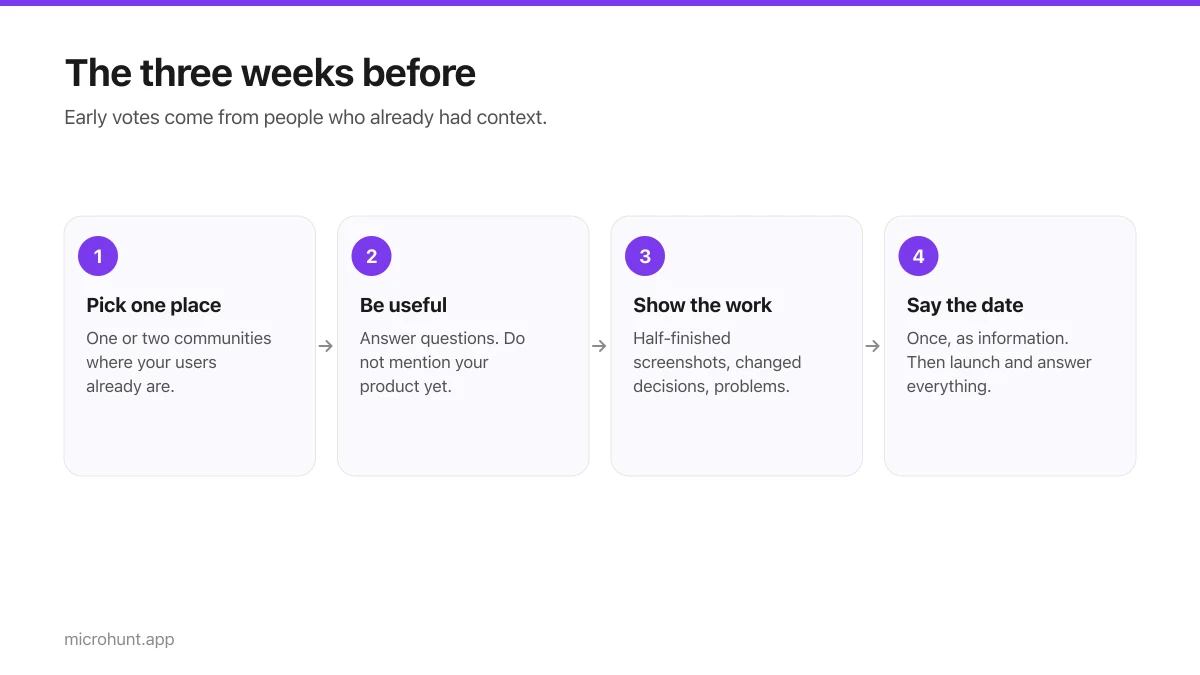
How to Get Your First Upvotes Without Begging
What actually generates early votes, why vote-for-vote groups do not work, and the approach that keeps paying off after launch day.
7 min read
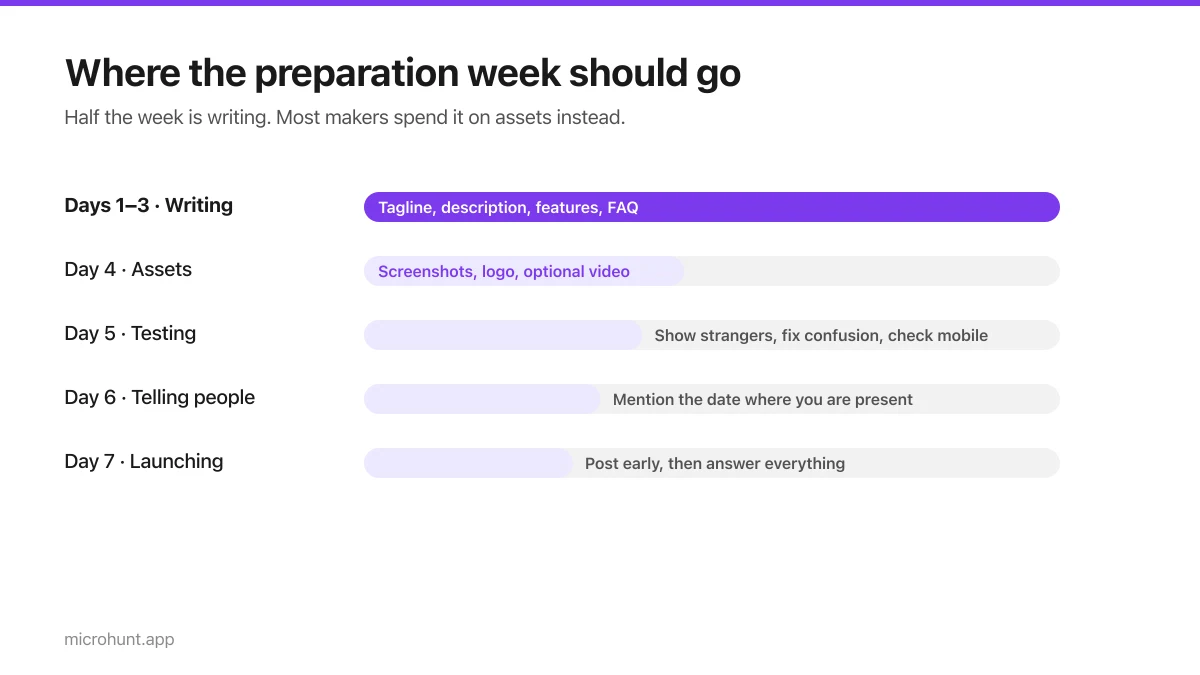
The Seven-Day Launch Checklist
A day-by-day plan for the week before you launch, weighted towards the things that actually change the outcome.
8 min read
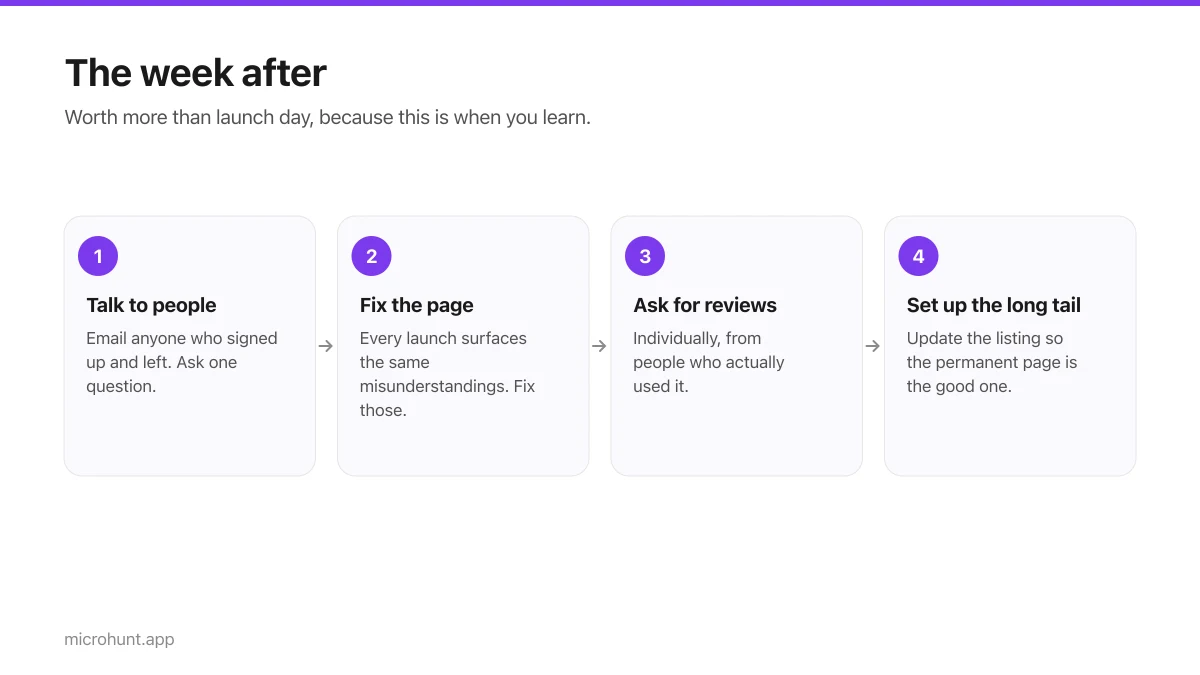
What to Do the Week After Launch Day
The traffic spike is over. Here is how to turn a day of attention into something that lasts longer than the graph.
7 min read